Book a Demo
Close
X-CTEM Platform

Know Every Risk. Act Before Attackers Do.

CyberCyte X-CTEM is the only platform that executes the full CTEM lifecycle — from discovery and prioritisation through to remediation — in one unified workflow.

Continuous Threat and Exposure Management

Organisations implementing a CTEM programme are three times less likely to suffer a breach. Yet most security teams still work in cycles. CyberCyte changes that. Our AI-powered X-CTEM Platform continuously identifies, prioritises, and closes exposures across your entire attack surface — so your security posture improves every day, not just after your next audit.

Traditional Tools Miss What Attackers Find First

Traditional vulnerability management tools miss complex artefacts including malicious DLLs, software library vulnerabilities, OS misconfigurations, and inactive or unhealthy security agents. CyberCyte eliminates the time gap.
73% of security incidents occur due to unmanaged or unknown assets.
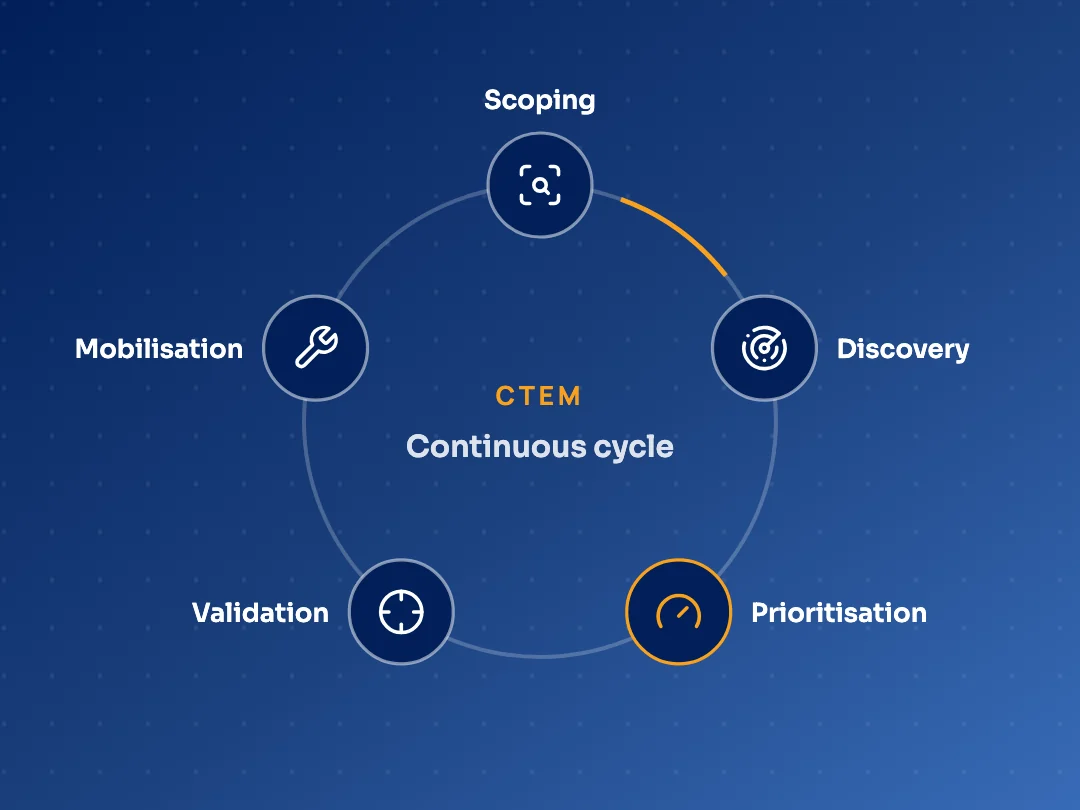
CTEM cycle: scoping, discovery, prioritisation, validation and mobilisation

The Full CTEM Lifecycle in One Platform

CyberCyte’s CTEM engine combines agent-based and agentless data collection with network scanning and technology integrations.

WHAT CYBERCYTE COLLECTSWHAT YOUR TEAM SEESEndpoints & serversWindows, Linux and macOS agentsNetwork devicesAgentless discovery over SNMP and NmapVulnerability scannersTenable, Qualys and OpenVAS resultsEDR / XDRCrowdStrike, Defender and Cortex healthIdentitiesActive Directory and Entra IDCloud & external surfaceAWS and Azure via Prowler, external assetsArtefact risk priority matrixMaliciousCriticalHighAI CriticalAI HighShadow ITRemediation jobPowerShell, SSH, patch or agent repairWaiting approvalRollback ready12345CTEM1 ScopingDefine assets, services and business priorities.
What CyberCyte collects
Endpoints & serversWindows, Linux and macOS agents
Network devicesAgentless discovery over SNMP and Nmap
Vulnerability scannersTenable, Qualys and OpenVAS results
EDR / XDRCrowdStrike, Defender and Cortex health
IdentitiesActive Directory and Entra ID
Cloud & external surfaceAWS and Azure via Prowler, external assets

Define assets, services and business priorities.

What your team sees
Artefact risk priority matrix
MaliciousCriticalHighAI CriticalAI HighShadow IT
Remediation jobPowerShell, SSH, patch or agent repair
Waiting approvalRollback ready

Everything You Need to Manage Threat Exposure

Over 500 artefacts across threats, misconfigurations, and vulnerabilities.

Attack Surface Visibility

Continuous internal and external attack surface visibility.

500+ Artefact Assessment

Comprehensive coverage including DLLs and software libraries.

AI-Driven Prioritisation

Intelligent classification mapped to business value.

Automated Remediation

PowerShell, SSH, patch and agent deployment.

Full CTEM Lifecycle

End-to-end from scoping through mobilisation.

Compliance Mapping

CIS, NIST, ISO 27001, DORA, NIS2, Cyber Essentials.

Measurable Security Improvement

3x
Reduction in breach likelihood (Gartner)
50%
Reduction in operational overhead
100%
Identification of unknown risks
24/7
Continuous posture improvement

See Your Exposure Now

Start a free assessment and discover the risks hiding across your attack surface.

Start Free Assessment